A security review should happen before a project becomes an emergency.
The right moment to review a system is not only after something has gone wrong. It is when the business can no longer clearly explain what is exposed, who has access or what would happen if an important part fails.
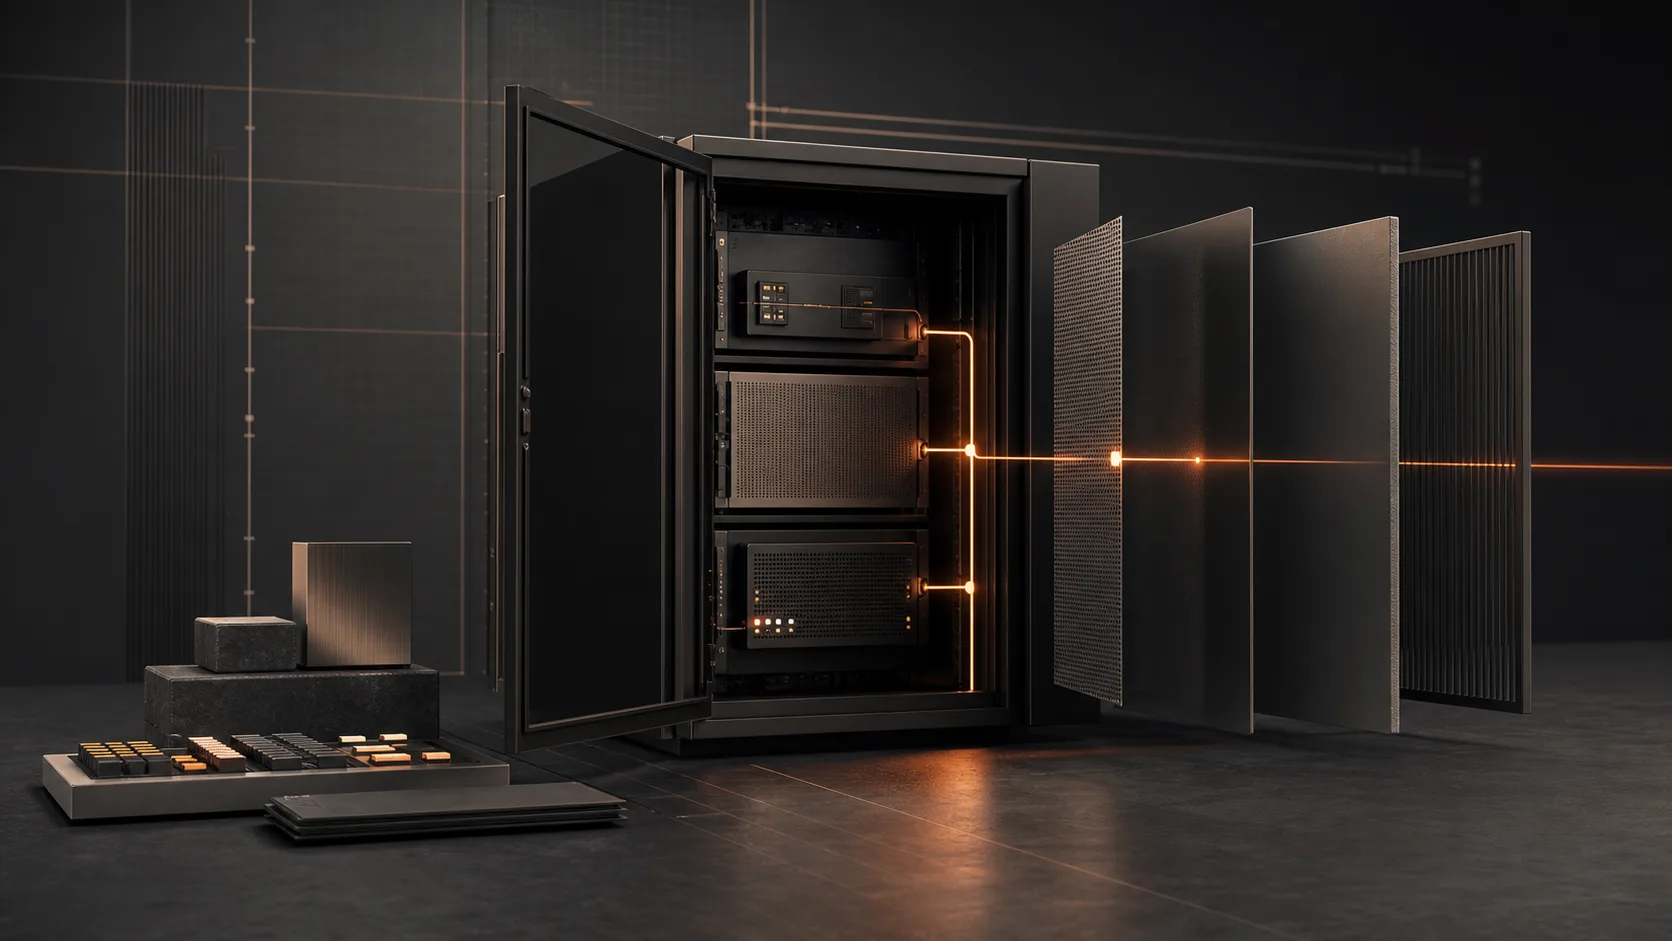
A security review is not a performance of breaking into something. It is a controlled way to understand whether a real business system is exposing more than it should, relying on weak assumptions or carrying technical risk that nobody has properly mapped.
Many companies ask for help late: after a suspicious login, a broken update, an inherited project with unclear access, an agency handover or a customer asking a difficult question. The urgent situation matters, but the more valuable work is restoring clarity before the next incident has a chance to become expensive.
The aim is practical risk reduction. We look at the systems the business actually depends on, agree what is allowed to be tested and turn findings into fixes that a team can understand and maintain.
Security work becomes useful when it replaces uncertainty with a clear order of risk, responsibility and next actions.
Three questions a responsible review should answer
A useful security engagement does not produce a dramatic list of technical words. It gives the business an honest picture of its exposure and a sensible sequence for reducing it.
What is exposed?
Identify the relevant public surface, important integrations, old endpoints, configuration gaps and data flows that need a closer look.
Who can do what?
Review authentication, roles, permissions, session behaviour and the places where an account could reach information or actions it should not control.
What should change first?
Prioritise findings by realistic business impact and ease of remediation, then verify the important fixes instead of leaving a report on a shelf.
When does a business need a security review?
A business should request an authorised security review before or after a major launch, when inheriting an older platform, after suspicious behaviour, before connecting sensitive systems, or whenever access rules and operational risk are no longer fully understood.
The trigger does not have to be a confirmed breach. A new payment flow, a customer portal, a multi-user dashboard, a migration, a third-party integration or a change in who administers the system can all change the risk profile. These are moments to ask whether the rules still match the reality of the project.
The right scope depends on the system. A public marketing site and a platform holding user accounts, operational data and payments deserve different depth. What matters is being explicit about the authorised targets, testing window, data handling, contact path and what must never be disrupted.
- Define the domains, applications, accounts and environments that are in scope before any testing starts.
- Agree a point of contact and a stop procedure for any finding that could affect availability or data.
- Treat inherited credentials, inactive accounts and abandoned integrations as review items, not administrative leftovers.
- Keep a written record of fixes, ownership and verification so risk does not quietly return with the next change.
Good security testing follows the application, not a generic checklist alone.
The OWASP Web Security Testing Guide groups web application testing around areas such as configuration and deployment, identity management, authentication, authorisation, session management, input validation, error handling, cryptography, business logic and client-side behaviour. That is a useful structure because real problems often appear where those areas meet.
For example, an account system can have a polished login screen while still handling a protected action incorrectly. A form can validate its visible fields while an integration accepts data in a way the user never sees. The review needs to follow the actual workflow and the decisions the software makes, not just a list of pages.
The report is not the outcome. The hardening plan is.
Findings should be understandable to the person responsible for the business, not only to the developer who will fix them. Each one needs context: what is affected, why it matters, how urgently it should be handled and how the fix will be verified.
Some improvements are small and immediate. Others need engineering work, operational changes or a rebuild of a fragile part of the system. Honest prioritisation is important: a team should know what needs attention now, what should be scheduled and what is simply good practice for the next development cycle.
The first deliverable is clarity, not alarm.
LineWeb security work is scoped around the business system that needs protection: difficult technical analysis, vulnerability discovery, practical hardening and a clear path from evidence to remediation.
Explore cyber security protectionClear answers, without the jargon.
01When should a business request a security review?+
A business should request an authorised security review before or after a major launch, when inheriting an older platform, after suspicious behaviour, before connecting sensitive systems, or whenever access rules and operational risk are no longer fully understood.
02What does a practical web security review cover?+
A scoped review commonly examines the exposed application surface, configuration and deployment risks, identity and access control, authentication and session handling, input validation, sensitive data handling, logging and the business logic around important actions. The exact scope should be agreed in writing before testing begins.
03Does a security review guarantee that a project is secure?+
No. Security is ongoing risk reduction, not a permanent certificate. A good review identifies findings within an agreed scope, prioritises remediation, verifies the important fixes and leaves the business with a clearer process for future changes.
Andrew Matia - LineWeb
Founder of LineWeb. I write about the practical side of websites, systems, automation and search: the decisions that make a business easier to run and clearer to find.
Read the founder storyGet a clear view of the system before pressure makes the decision for you.
We can define an authorised scope, examine the relevant risk and turn the findings into a practical hardening plan.